
Yandex outage coincided with malicious bot movement
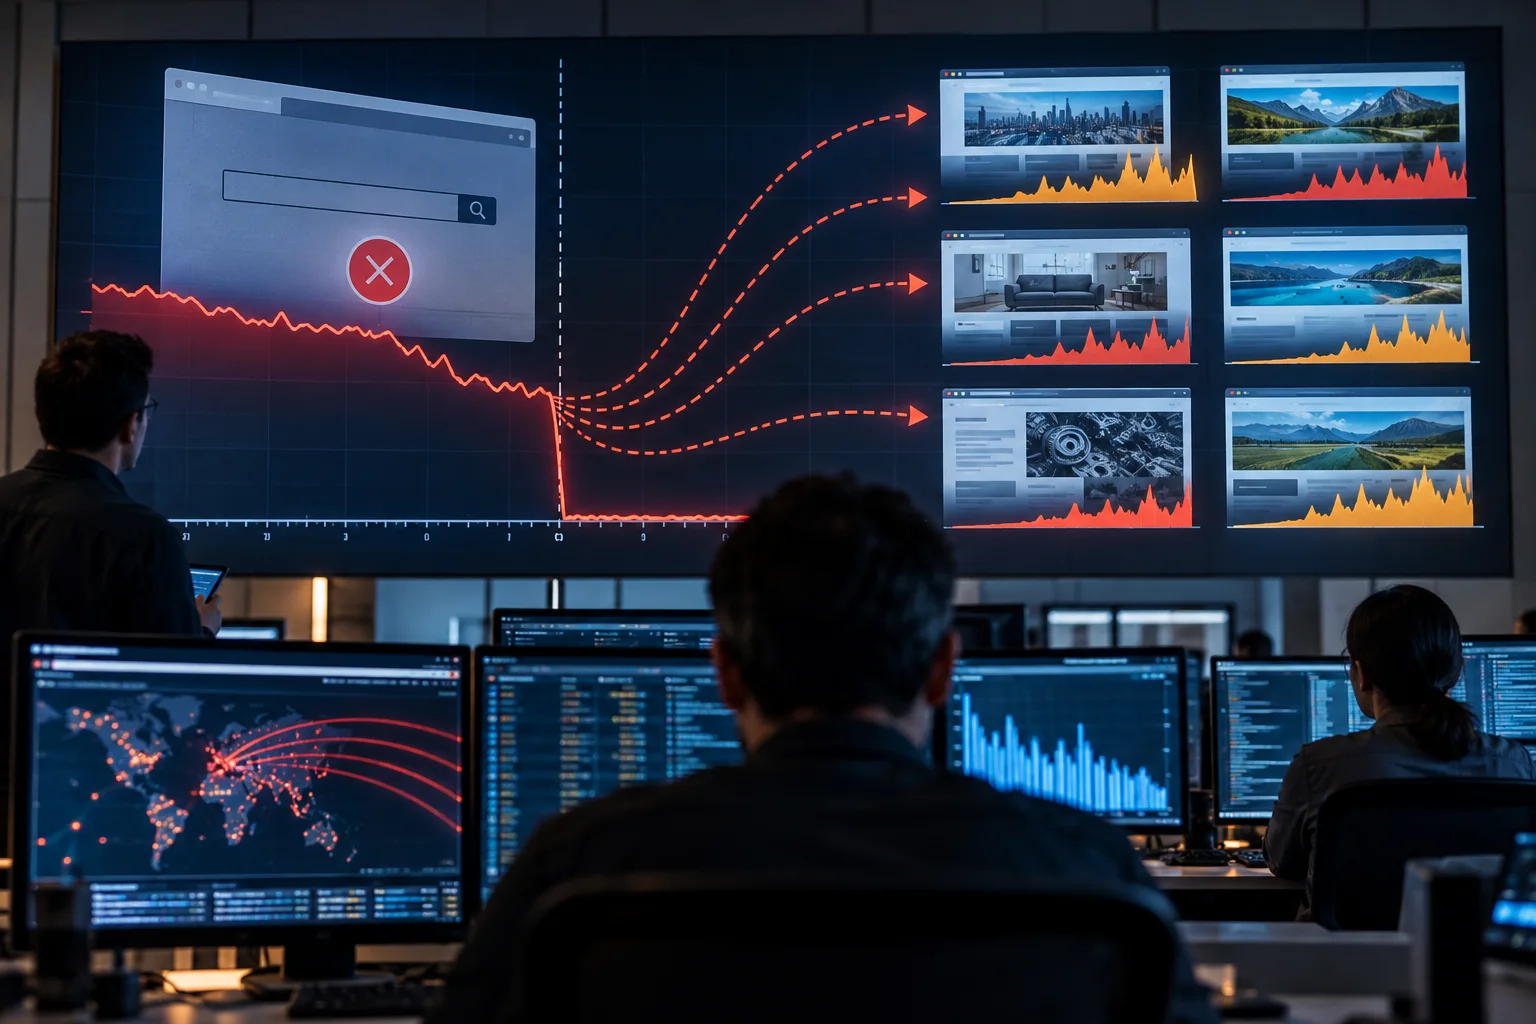
The Yandex outage coincided with malicious bots shifting their activity rather than simply disappearing, according to analysis published by Cloudflare on October 14, 2026. A bot is software that makes automated requests or performs online actions without a person operating each one. Cloudflare described the bots in this case as malicious, meaning the automation was associated with harmful activity rather than legitimate functions such as search indexing or service monitoring.
The central finding changes how an outage should be interpreted from a security perspective. An outage is a period when a service is unavailable or seriously disrupted. It may reduce normal traffic to the affected service, but Cloudflare's analysis indicates that hostile automation can remain active and move elsewhere. The bots connected with this incident did not simply go dark with Yandex. Cloudflare's description does not, by itself, identify where every bot went, what actions each one performed or what caused the outage, so those points should not be treated as established.
For website owners and IT teams, the practical lesson is that service availability and malicious activity are separate things to monitor. A dashboard showing that a service is offline may explain a traffic drop, but it cannot show whether automated abuse has stopped or shifted to another destination. Teams should continue watching other websites, applications, login systems and public interfaces during an external outage rather than assuming that reduced activity in one place represents a broader reduction in risk.
This is where observability, the collection of information that helps operators understand what a system is doing, becomes important. Availability checks answer whether a service responds, while traffic metrics show quantities and patterns of requests. Logs, which are time-stamped records of system events, can show what was requested and whether repeated attempts reached login pages, forms or other exposed parts of a website. Alerts can then notify staff when activity departs from an expected baseline, meaning the normal pattern used for comparison.
The Yandex outage also illustrates why monitoring one total traffic figure is not enough. If automated requests leave one destination and appear elsewhere, an overall decline may conceal concentrated activity against another system. Operators should compare traffic across services and examine the type of requests being made, not just whether request volume is rising or falling. That analysis must remain evidence-led: a change during an outage is a signal to investigate, not automatic proof that the outage caused the change or that every automated request is hostile.
Incident procedures should therefore cover more than restoration of the unavailable service. Teams can preserve relevant logs, check whether alerts fired, examine authentication attempts and review activity against forms or other publicly reachable functions. They should also document when changes began and ended so that traffic patterns can be compared with the outage timeline. This gives responders a clearer basis for distinguishing ordinary disruption from bot activity that has moved to a different target.
Website owners without a dedicated security team can still apply the same principle. During a major third-party outage, they can check the traffic and security views provided by their hosting or website-management service, look for sudden increases in repeated requests, and ask their provider to investigate unexplained changes. Administrative accounts should use two-factor authentication, which requires a second confirmation in addition to a password, because automated attempts commonly focus on exposed sign-in pages.
For organisations that need external help reviewing this wider operational risk, AEU-I provides security-first IT, infrastructure and consulting. The broader conclusion from Cloudflare's analysis is straightforward: when an online platform becomes unavailable, defenders should keep monitoring the rest of their environment because malicious bot activity may move rather than stop.